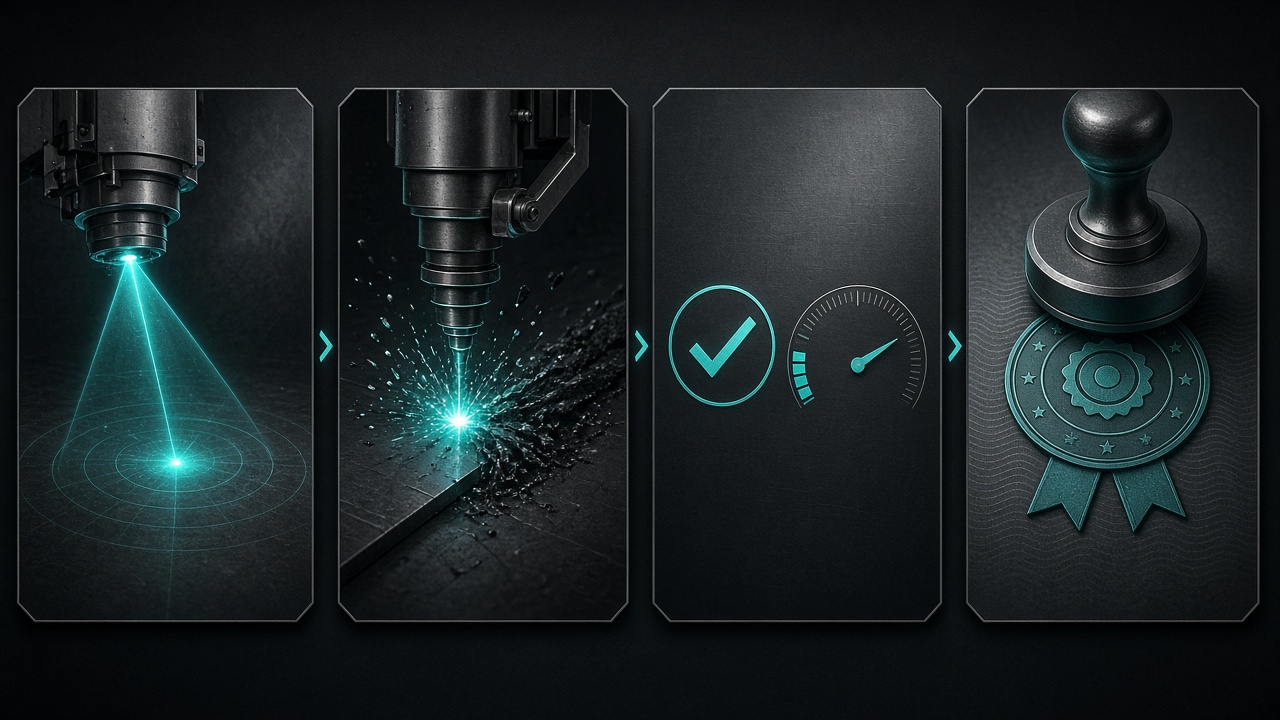
- 01 LocateExpand identity. Find refs.
- 02 EraseDelete, anonymize, or shred.
- 03 VerifyFresh read must be empty.
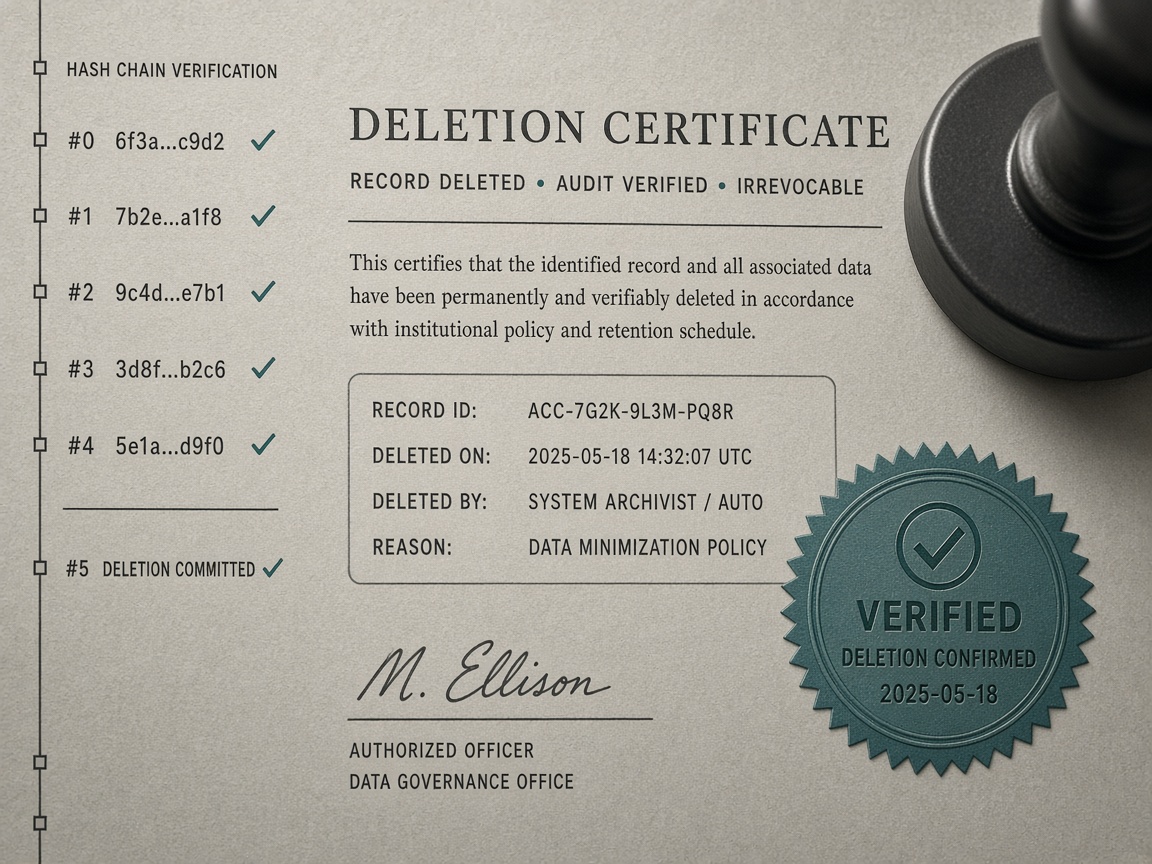
- 04 CertifySign. Timestamp. Seal.
Data map
You declare the estate.
A versioned shredproof.yaml names each source and action. Discovery flags gaps; it never deletes what you did not map.
subject:
  primary_key: customer_id
sources:
  rds.core:
    kind: postgres
    tables:
      customers: { action: delete }
      invoices:  { action: retain, basis: tax_7y }
  s3.uploads:
    kind: s3
    action: delete_all_versions
v1 sources
AWS first. Same trait forever.
New clouds are new crates; the certificate model does not change.
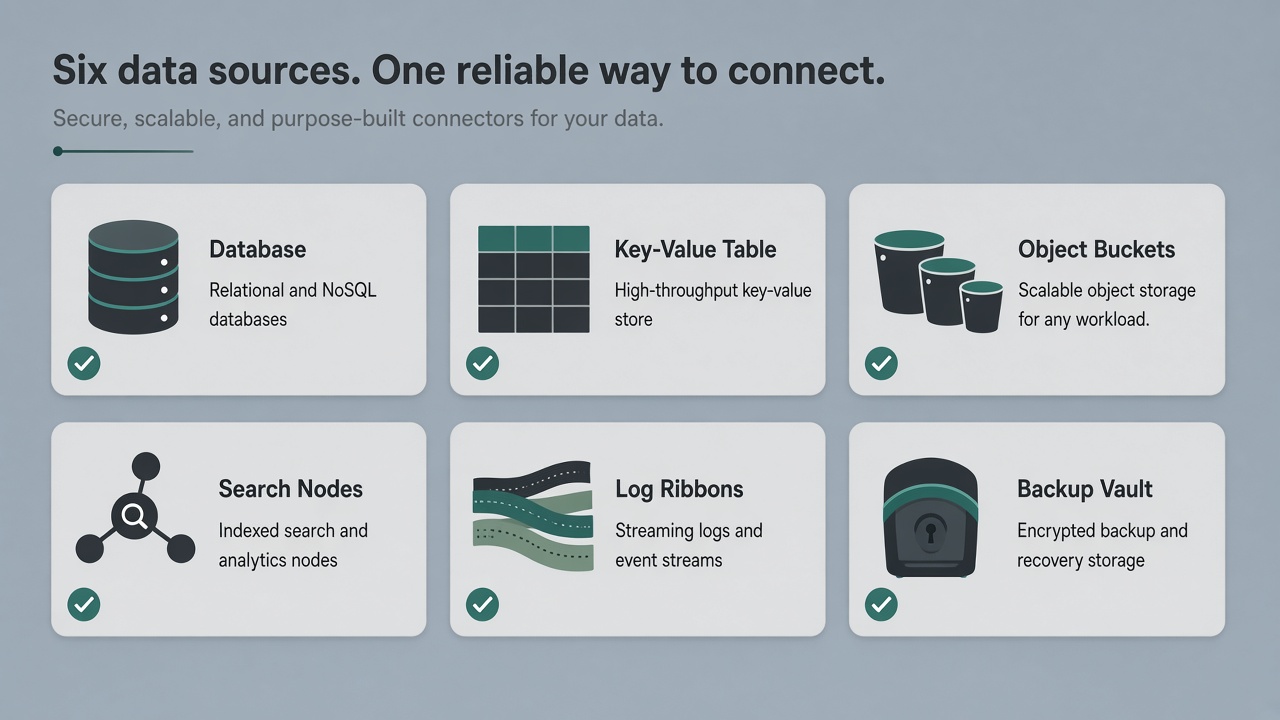
- RDS / Aurora
- DynamoDB
- S3
- OpenSearch
- CloudWatch Logs
- AWS Backup
Backups
 Crypto-shred
 Tombstone on restore
Two honest methods.
Crypto-shred makes every copy unreadable at once. Tombstone replay suppresses the subject when a backup is next restored.
Crypto-shred
Tombstone on restore
Certificate
Evidence, not an email.
JCS + DSSE, your KMS key, RFC 3161 timestamp. Offline verify. No PII; subject is an HMAC.
Run it on a synthetic subject